Boostara Medical AI

Please enable JavaScript to use this site. Download the Boostara App on Google Play

Skip to main content Skip to main content
Boostara Innovations Logo
BOOSTARA MEDICAL AI
BY BOOSTARA INNOVATIONS
Medical Data Sovereignty Architecture

In-App Encrypted Vault & Zero-Knowledge Architecture

Unlike public web chatbots where sensitive clinical data can leak into model retraining pools, Boostara Medical AI enforces absolute client-side data sovereignty: all patient health records, diagnostic images, and clinical reports are stored and encrypted directly inside your local Boostara App Vault.

End-to-End Architectural Data Flow

How Data Moves: Device to Ephemeral Inference

USER DEVICE
Scan captured or DICOM loaded
TLS 1.3
EPHEMERAL RAM
Volatile memory buffer only
MODEL
IN-APP VAULT
Sealed with device biometric key
• Local Device Storage: Raw patient records and exported reports reside exclusively on the clinician's authenticated physical device.
• Controlled Ephemeral Processing: When cloud inference is requested, packets traverse a pinned TLS 1.3 encrypted tunnel into isolated volatile RAM. Zero hard-drive caching; memory is zeroized upon token stream completion.
• Zero Model Re-Training on PHI: Patient images are never aggregated or used to re-train public foundation models without explicit institutional research agreements.
1. The In-App Vault Principle

Users must install the Boostara App on their device (Android phone, iPhone/iPad, Windows workstation, or Linux PACS server) to authenticate and communicate with our Cloud AI.

  • Local Storage: Scans, DICOM series, and AI findings are held in an isolated device sandbox.
  • Hardware Enclave Keys: Encryption keys are bound to device biometrics (Fingerprint/FaceID or TPM 2.0).
  • Offline Access: All saved historical scans and reports can be reviewed offline without an active internet connection.
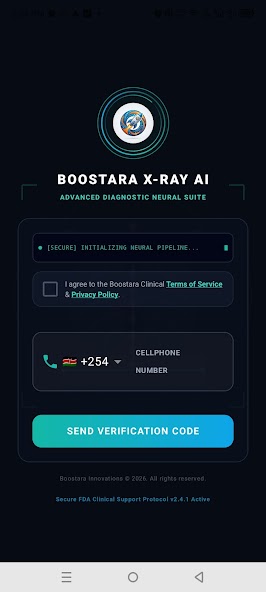
Clinical Authentication Shield
FDA Protocol Auth Shield
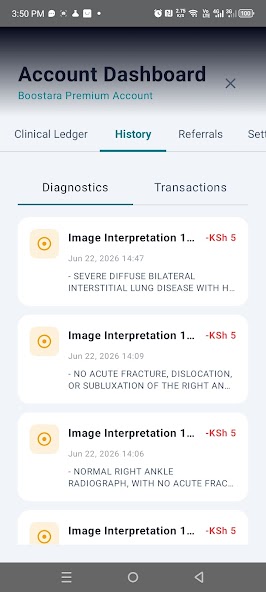
In-App Local Encrypted Vault Records
Encrypted Patient Vault History
Local Client Vault Cryptography
Cipher: AES-256-GCM (Galois/Counter Mode)
Key Derivation: Argon2id (m=64MB, t=4, p=4)
Auth Tag: 128-bit GHASH Authentication Tag
Payload Integrity: SHA-256 Cryptographic Hash Chain
Hardware Security: Android Keystore / Apple Secure Enclave
Ephemeral Cloud AI Execution Loop
1. Client TLS 1.3 Handshake (Pinned Certificates)
2. Ingestion into Volatile Memory (RAM Isolation)
3. Model 19 Inference Execution (<180ms)
4. Differential Diagnosis & Heatmap Stream to App
5. Immediate Memory Zeroization & Purge (0 Server Storage)

2. Ephemeral Cloud AI Processing

When a clinician submits a scan for multi-modality evaluation, the image payload is transmitted over an encrypted TLS 1.3 tunnel directly into hardware-isolated volatile memory (RAM).

Once neural inference completes and findings stream back to the clinician's device, the cloud memory buffer is immediately zeroized. Zero unverified patient records are persisted on cloud disks.

Regulatory Framework Compliance

Kenya Data Protection Act 2019

Full adherence to Part IV principles of data protection, sensitive health data processing safeguards, and local data sovereignty guarantees.

HIPAA Security Rule

Enforces technical safeguards: access control, transmission security, end-to-end encryption, and cryptographic audit controls for protected health information (PHI).

EU GDPR (Article 9)

Special category health data processing compliant with strict explicit consent mechanisms, right to erasure, and zero-knowledge data retention architectures.

Chat on WhatsApp

Clinical Disclaimer: Boostara Medical AI products are AI-assisted decision support tools intended for use by qualified licensed healthcare professionals. They are not a substitute for professional medical advice, clinical diagnosis, or treatment. All AI-generated findings must be reviewed and validated by a licensed clinician. Not cleared as a medical device. For support: support@boostarainnovations.co.ke